$ ls /blog
Blog
Technical deep dives, practical lessons, personal experiences, and the occasional random thing worth sharing, all shaped by real-world experience and curiosity.
/ posts
12 posts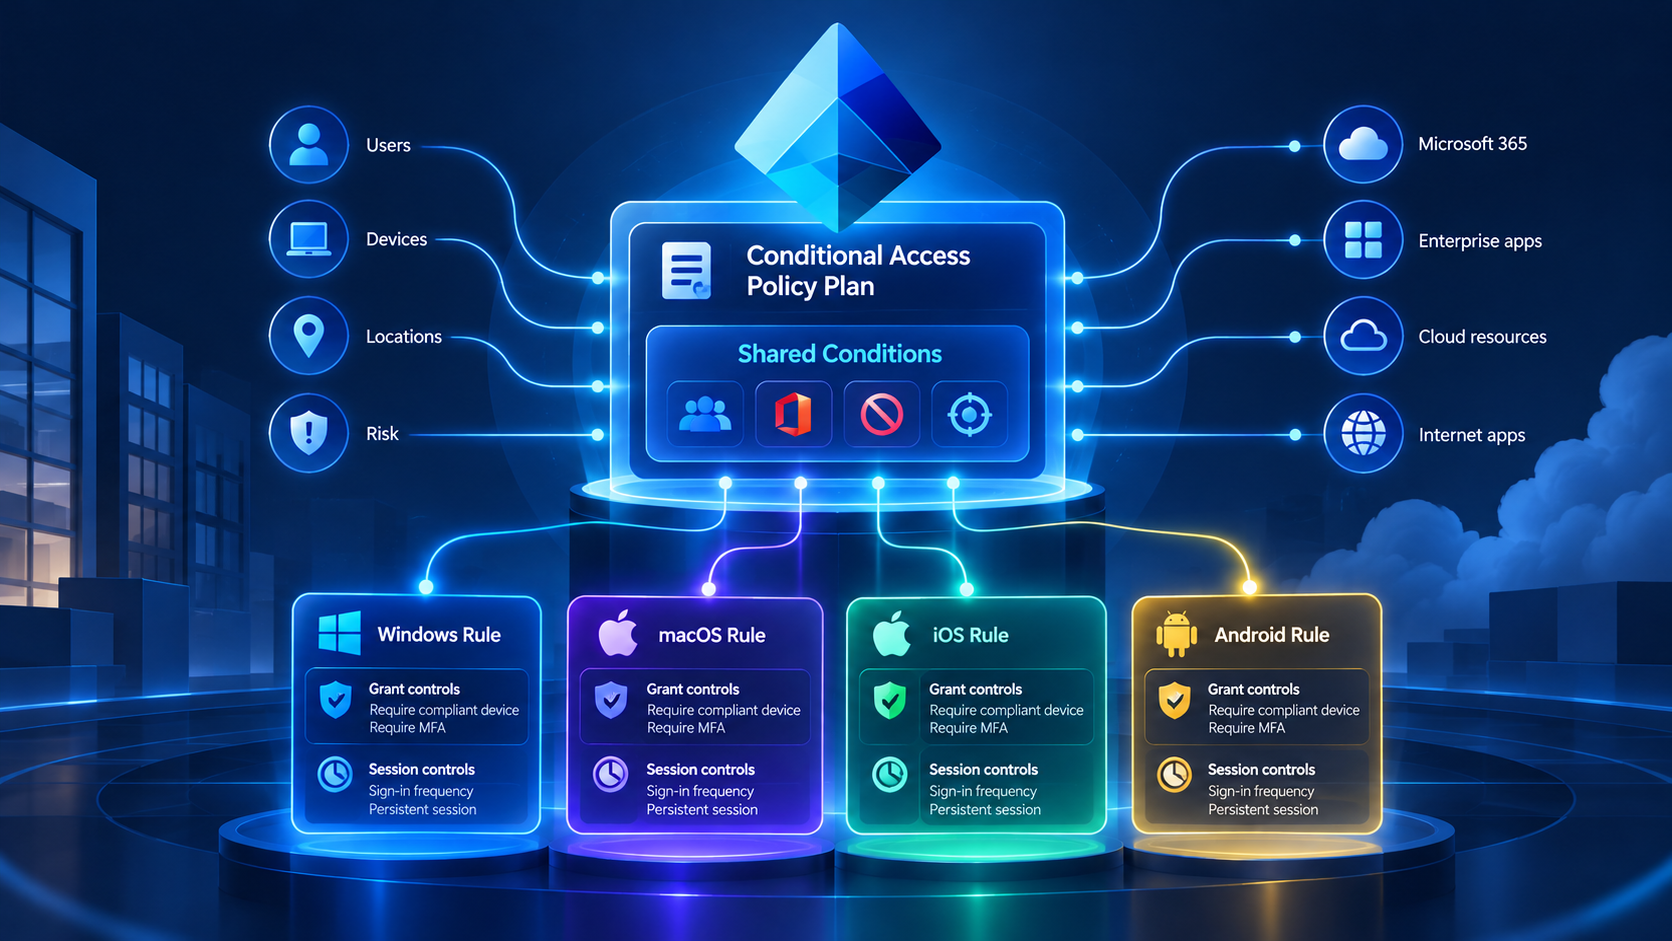
Microsoft Entra Conditional Access Policy Plans
Exploring Microsoft Entra Conditional Access Policy Plans, shared conditions, independent enforcement, and migration
The Defender Agent [Lab Part 8]
How the Helixora defender agent reviews a separate audit stream, summarizes and investigates meaningful signal groups, and classifies detection visibility without reading the offensive findings.
The Validation Agent [Lab Part 7]
How the Helixora validation agent independently retests findings, records confirmed, rejected, or inconclusive outcomes, and uses safe verification techniques without trusting application-provided explanations.
The Analysis Agent [Lab Part 6]
How the Helixora analysis agent correlates identities, directory roles, credentials, API authorization differences, and business programs to turn isolated findings into an evidence-backed attack story.
The Application Security Specialist [Lab Part 5]
How a conditionally invoked application-security agent performs bounded follow-up on reflected XSS, IDOR/BOLA, PII exposure, debug disclosure, and weak password recovery without duplicating reconnaissance findings.
Reducing AI Token Usage with Caching
Explore how prompt caching, application caching, retrieval, context management, and better prompt design can reduce token usage when building applications with OpenAI, Claude, Gemini, and Grok.
The Reconnaissance Agent [Lab Part 4]
Follow the Helixora reconnaissance agent as it discovers staging, exposed configuration, employee information, API documentation, anonymous shares, credentials, and recovery metadata.
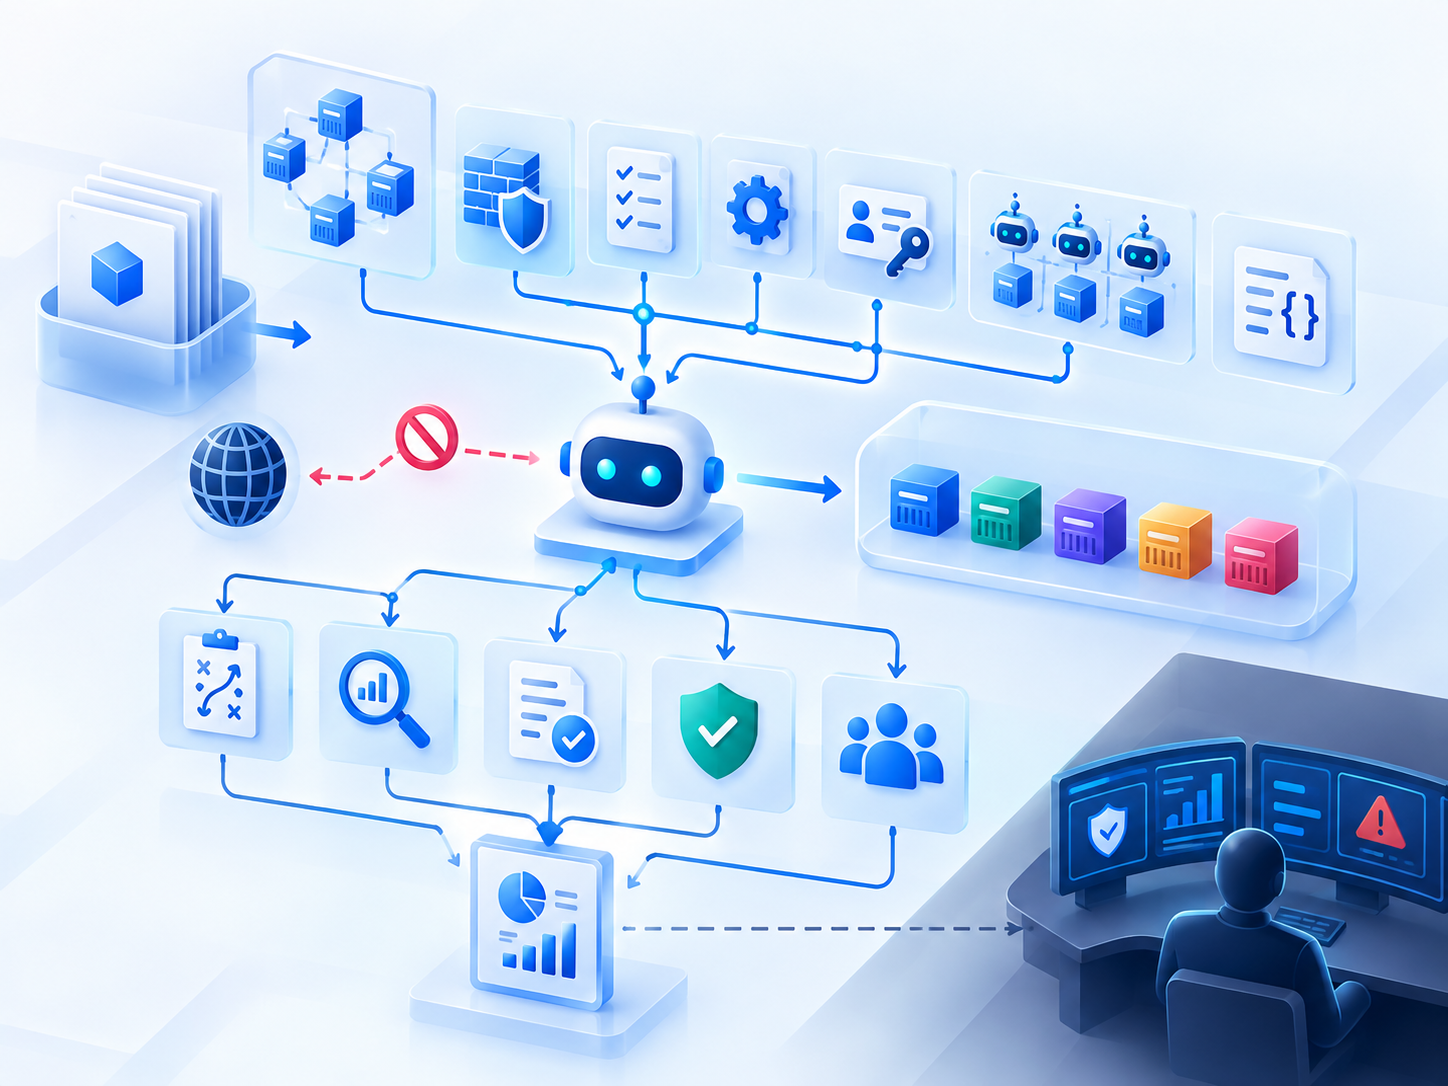
Designing Safe Tools for Security Agents [Lab Part 3]
How the Helixora learner lab constrains AI security agents with an explicit hostname allowlist, bounded enumeration, role-specific tools, local services, human approval, and auditable evidence.
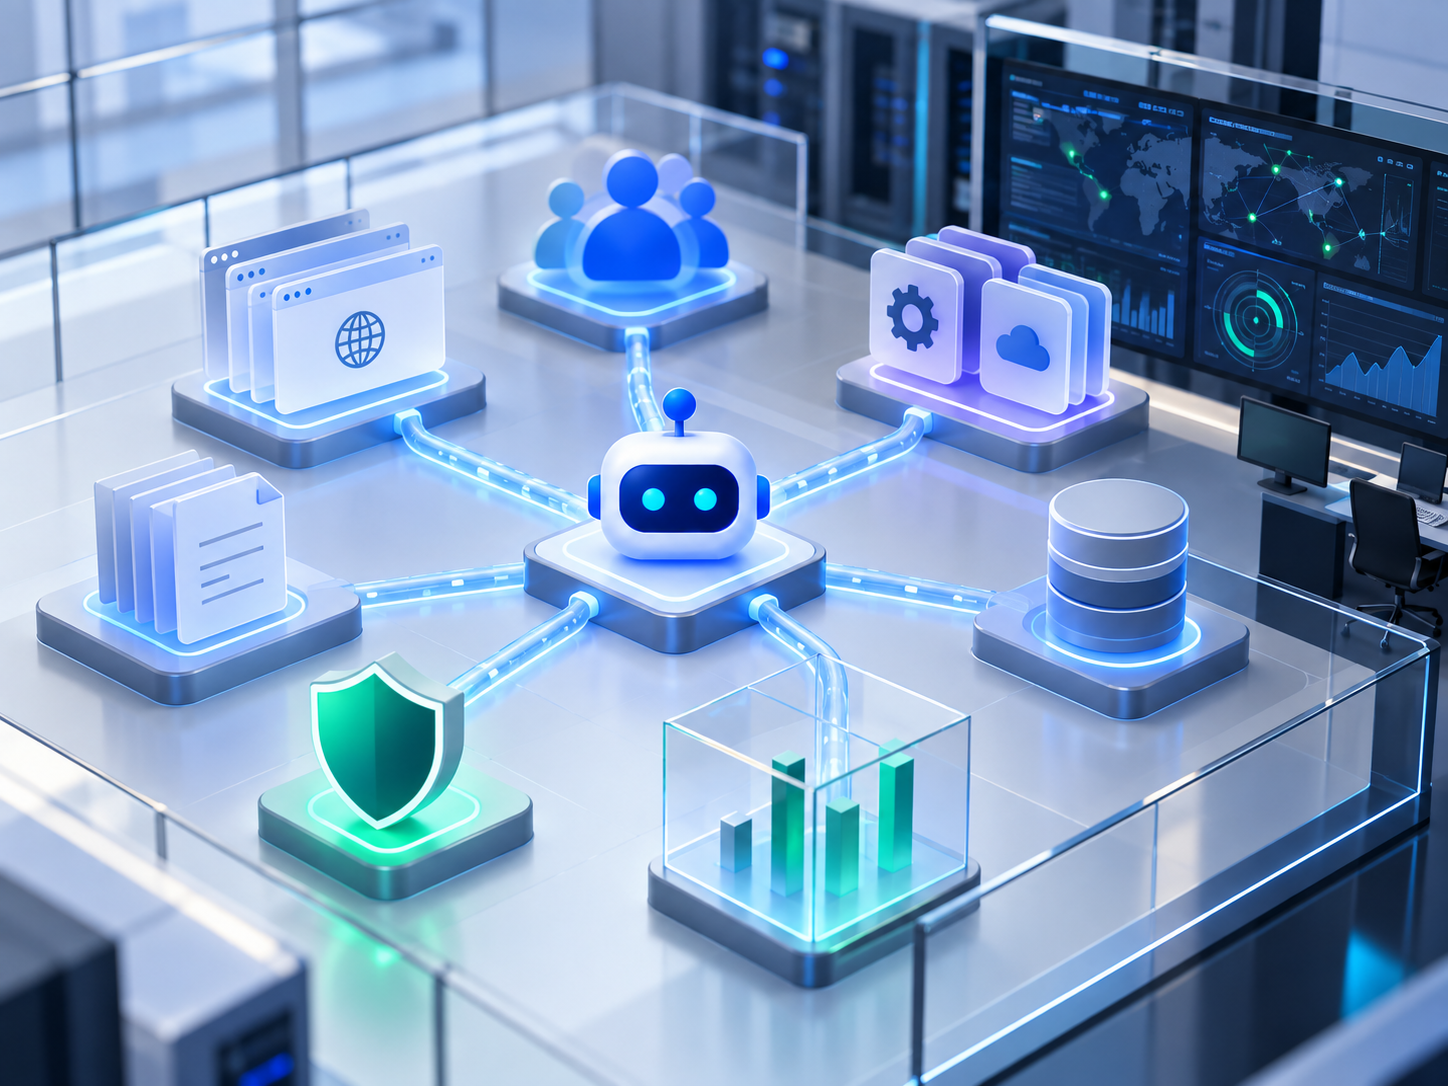
Inside the Lab [Lab Part 2]
A guided tour of the fictional applications, identities, APIs, evidence, and defensive telemetry inside the self-contained AI agent reconnaissance lab.
Conditional Access for AI Agents
Exploring how Microsoft Entra Conditional Access extends Zero Trust controls to AI agents, agent identities, autonomous access, and agent user accounts.
AI Agents for Security Reconnaissance [Lab Part 1]
Exploring how AI agents can transform the reconnaissance phase of security assessments by orchestrating discovery and reasoning about the environment.
Metasploit Framework 6.5: What's New and Why It Matters
Metasploit Framework 6.5 brings a collection of improvements across the framework, including authentication, Active Directory, credentials, payloads, modules, and post-exploitation capabilities.